MedusaLocker is a malware that is extremely active at the time of writing, including within France. It first appeared in September 2019 and has made a major comeback this year. This type of threat belongs to the RaaS (Ransomware-as-a-Service) family, allowing attackers to outsource the tedious and risky tasks of development and ransom collection associated with any malware campaign. There are many variants associated with this threat.
It is in this context that a currently active variant was detected by one of TEHTRIS' EDR (Endpoint Detection and Response) solutions and automatically sent to the CTI (Cyber Threat Intelligence) team for analysis. Our reverse engineers were then able to add configuration extraction capabilities for this variant.
What exactly is TEHTRIS doing about this pressing threat?
- Identification : Once detected, this malware is indexed in the sandbox , allowing analysts to immediately identify the source of the threat.
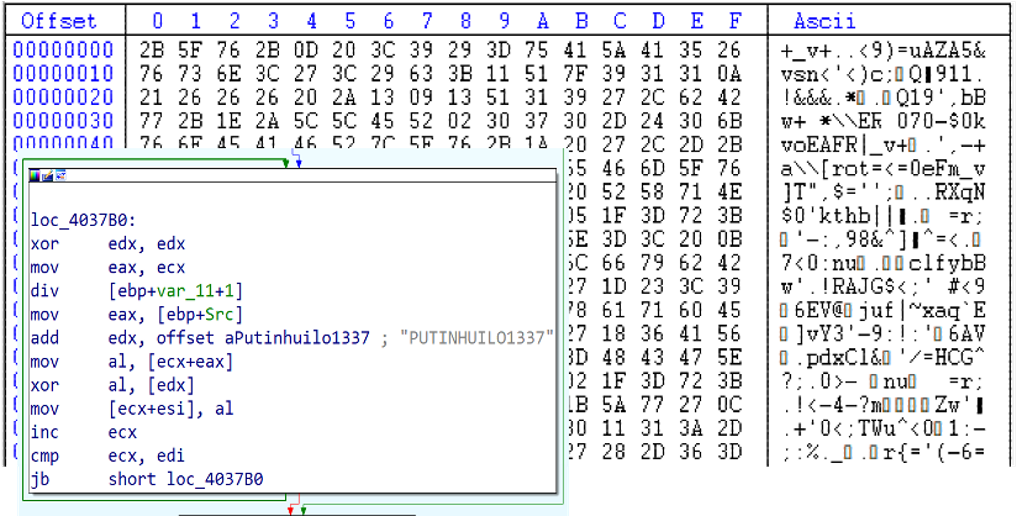
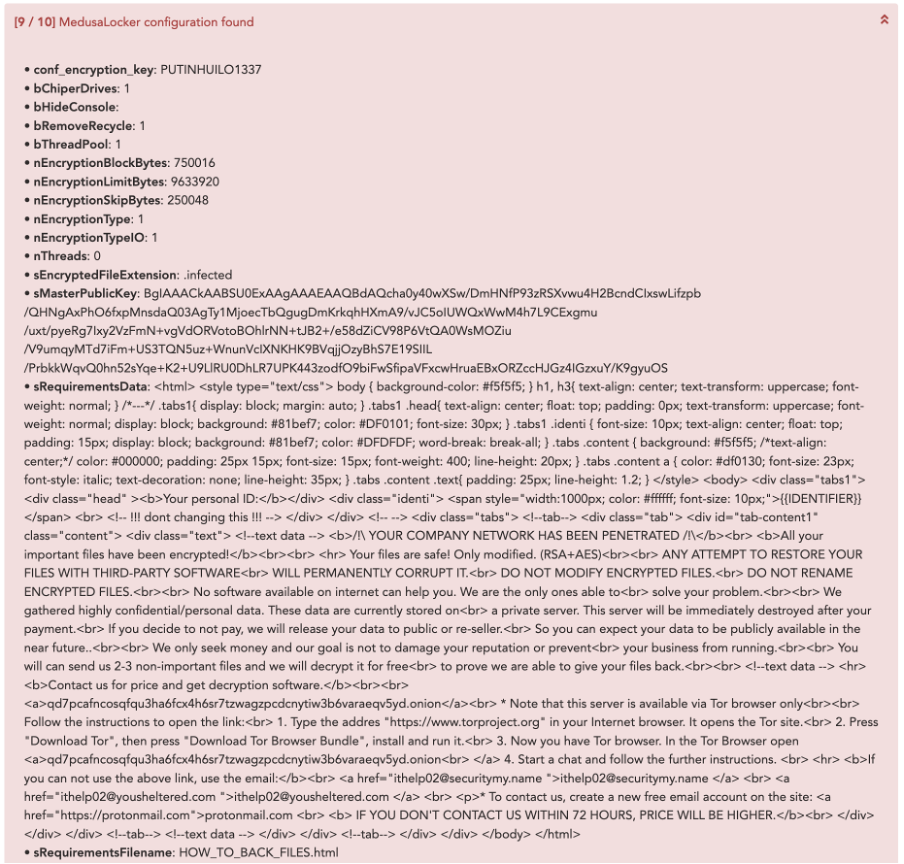
- Malware configuration deobfuscation : Since the malware in question uses obfuscation (T1001) to render its configuration unreadable, the dynamic analysis tools of the TEHTRIS sandbox allow for the decryption and display of the complete malware configuration to the analyst. They can then retrieve the executed commands, the files to be encrypted, the ransom note, ignored paths, the cryptographic key, and the performance features associated with the campaign corresponding to the analyzed malware. An example is shown below, comparing the obfuscated configuration with the one automatically extracted for the analyst.
MedusaLocker configuration:
Excerpt of the malware configuration displayed by the CTI tool:
IOCs (Indicators of Compromise):
- 51b8a283f87a95edb5e98125e5730bcf843fc7ec8fcdc175c8dc0ba3032e8a51
- c1d4014e65a8d79e555378dbf8e5db5786e3b6e4c841f7f64a3f40318bb59e60
- d9de562ac1815bf0baad1c617c6c7f47d71f46810c348f7372a88b296d68cfae
- 951facf3f3ef6f6163aa87383953132563d8ef1508b60cb130b1b7d5b96552aa
- f584c124d92b09ba12d2538d52300dc38ef255c6ad23c30e7569ff1920388c50
- b896605b97ae9e2781b21dc5cfb64eec0fc4effa76a7ef33e9cef0b258dff35f
TEHTRIS CTI (Cyber Threat Intelligence) is an extensive threat knowledge base. This database has existed since 2014 and has undergone numerous technical evolutions to keep pace with or stay ahead of new offensive developments.
TEHTRIS CTI, integrated by default into the TEHTRIS XDR Platform.
TEHTRIS CTI has a unique feature: its integration is completely native to the TEHTRIS XDR Platform, meaning all our tools (EDR, EPP, SIEM, etc.) are immediately and systematically connected to it.
As a result, TEHTRIS CTI is not only capable of enriching your defensive cyber arsenal and providing analysis, hunting, and forensic investigation capabilities, but it also feeds on information shared between TEHTRIS client environments and various external knowledge bases.
TEHTRIS CTI offers you a broader, continuously updated view of threats, enabling a cybersecurity posture that is both robust and relevant.