Although they were relatively quiet until their recent attacks, LAPSUS$ has already claimed several world-renowned victims.
Having seemingly emerged in 2020, the group uses Portuguese in its communications and is believed to be based in South America. Until now, its members primarily targeted smaller organizations.
What makes the LAPSUS$ group unique
The unique characteristic of this group, which has been making international headlines in recent weeks, is that they do not seem interested in developing ransomware, but rather in direct data theft.
The LAPSUS$ group likes to stand out for its originality and does not use the traditional Dark Web communication channels, preferring two Telegram channels where they have a combined total of 33,000 subscribers.
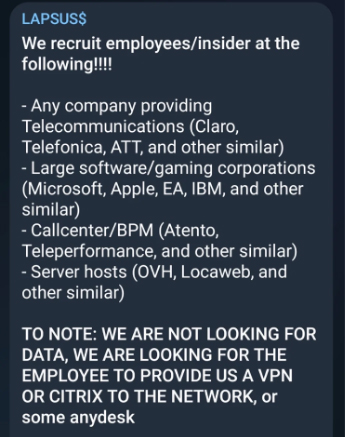
The group's members do not hesitate to advertise their recruitment, and have openly announced they are looking for insiders at various companies, particularly in the telecom and software publishing sectors, including Microsoft, Apple, EA, AT&T, and more. This type of communication is not very surprising, as the group is suspected of using internal employees to facilitate their attacks.
Major attack campaigns
Although the LAPSUS$ group has remained very discreet until now, no one in the cyber world can ignore them.
Their list of victims is growing dangerously long, and includes:
- Impresa media: LAPSUS$ published a message directly on their website demanding a ransom.
- The Brazilian Ministry of Health, a victim of the group last December, saw its servers shut down.
- Vodafone
- MercadoLibre, where 300,000 user records were stolen.
- LG: The group threatens to leak employee passwords.
- Ubisoft…
Let's take a closer look at the last 4 attacks.
NVIDIA
NVIDIA is an American company that designs GPUs (Graphics Processing Units). These are computer chips located on the graphics card, designed to optimize 2D and 3D display.
The American company suffered an attack on February 23, 2022. The group suspected of being behind this assault is none other than Lapsus$. They reportedly possess 1TB of data regarding the company's or its clients' projects, including certificates that allow NVIDIA to sign its binaries. These certificates have also been used by attackers to sign their malware, making it appear as legitimate NVIDIA software.
Their attack technique seems different from most groups, as they reportedly rely on internal moles to carry out their misdeeds. In this case, they were able to access information systems for over a week via an employee's VPN.
MICROSOFT
On March 22, 2022, Microsoft confirmed that one of its employees had been compromised by the Lapsus$ hacking group.
The haul: 37 GB of source code stolen from Microsoft's Azure DevOps server.
The group confirmed the theft by posting screenshots on Telegram. The data includes a folder related to Cortana (the group claims to hold 45% of the data) and projects related to the Bing search engine (the group claims to hold 90% of the source code)…
Microsoft link: https://www.microsoft.com/security/blog/2022/03/22/dev-0537-criminal-actor-targeting-organizations-for-data-exfiltration-and-destruction/
SAMSUNG
On Monday, March 7, 2022, it was Samsung's turn to report a data breach. Part of the source code for Galaxy devices was leaked. The attack reportedly originated from a vulnerability found within that same source code.
Lapsus$ went further, claiming to hold 190 GB of confidential data from the electronics giant, which currently accounts for 19% of global smartphone sales.
The impact is massive, as hundreds of millions of users could potentially be affected. Samsung has provided reassurance, stating that no personal customer information was compromised.
OKTA
Okta is a specialist in identity and access management as a service.
To date, they have 15,000 customers worldwide, including Zoom, AWS, Confluence, Splunk, Salesforce, and Jira.
The attack on Okta was announced on March 22, 2022, by Lapsus$ (the breach having been detected in January), a group that continues to expand its list of targets. The group reportedly had access to the laptop of an engineer working for a third-party provider for 5 days (source: Mag IT).[1].
Nevertheless, the access management specialist confirms that there has been no compromise. Once again, Lapsus$ confirmed this attack via a screenshot. From these attacks, we can infer that the hacker group LAPSUS$ is increasingly active and likely to cause alarm in the coming days. These attacks could serve as a springboard for other threats, particularly supply chain attacks.
Ultimately, security measures must be more active than ever and implemented in every company, particularly regarding digital hygiene practices, user behavior, and internal competitive intelligence.
The threat can come from within. The zero trust concept has never been more aptly named.
Protection solutions
Protection solutions must be activated more than ever when facing such a formidable enemy.
We can only reiterate the importance of adopting the right security mindset.
This involves the five key pillars:
- Implementing multi-factor authentication
- Securing VPNs
- Securing the Cloud
- Segmenting your assets
- Ensuring endpoints are healthy, reliable, and well-protected. This is what TEHTRIS offers with its XDR technology
And finally, improving internal awareness of attacks, as the threat comes from everywhere. Lapsus$ chose the internal route, and it is clear that it works.
Valery Marchive. Lapsus$: Okta reports a "failed attempt" at compromise. 2022 & Lapsus$: Okta reports a "failed attempt" at compromise